Acronis CISO: Partner’s access to customer data makes them “attractive” to attackers
New Acronis CISO Gerald Caron explains to CRN Australia how he sees the current threat landscape.
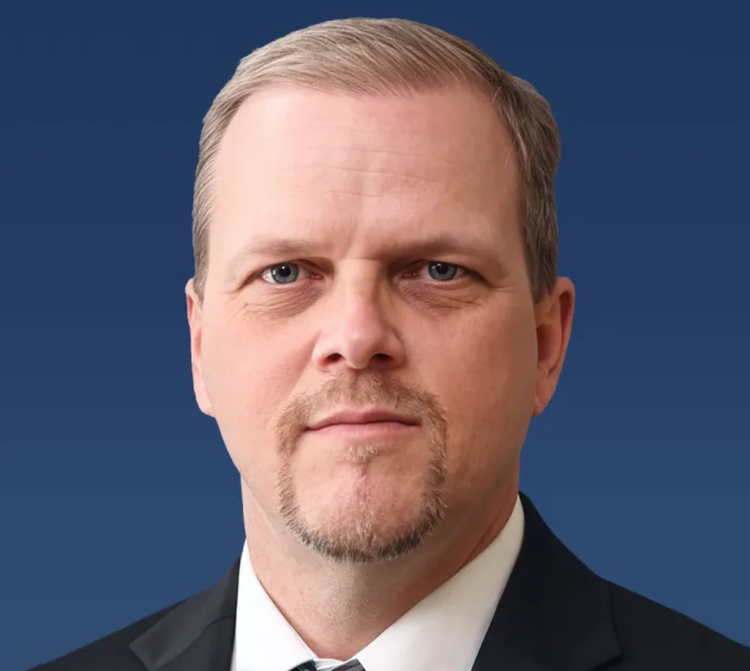
Clients are entrusting MSPs with access that could also put their business at risk, according to new Acronis CISO Gerald Caron.
The tools MSPs are relying on could also be a backdoor for bad actors, according to the CISO.
Caron highlighted an Auto IT incident that happened last month. He said it affected a small number of customer environments involved unauthorised use of a third-party remote monitoring and management tool.
“A capability intended to support customers became part of the incident. That gives clients a concrete reason to ask how their provider protects administrative access, separates customer environments and detects misuse,” he said.
“They also need to know who takes charge during an incident and how essential services will continue.”
Caron added that MSPs should expect to demonstrate those capabilities through clear reporting and recovery exercises.
“Trust increasingly depends on being able to show how the service performs under pressure,” he noted.
MSPs have the access to many backdoors and customers, which Caron said makes them “attractive” to attackers.
“A compromised management account or shared platform can create exposure across several clients, each with different systems and response requirements,” he said.
“Coordination matters here. Providers need established escalation channels with suppliers and national cyber authorities before an incident occurs.”
“An individual client may see one suspicious login, while a provider or Australian Signals Directorate’s ACSC may recognise a wider pattern. Sharing technical findings can help connect those observations and give other organisations an earlier opportunity to act.”
On the other hand, Caron said partners can make threat intelligence useful at the point where a client needs to make a decision.
“ASD’s March 2026 advisory on INC Ransom described attackers gaining access through spear phishing, unpatched internet-facing devices and credentials purchased from access brokers,” he said.
“For an MSP, that should trigger a review of affected clients, exposed systems and potentially compromised accounts.”
There is also room to build deeper expertise in particular industries for MSPs.
Caron highlighted another breach in June this year, a ransomware attack on Mackay Sugar disrupted milling operations and harvesting arrangements, extending the impact to growers and contractors.
“A group known as The Gentlemen claimed responsibility. Its broader operating model combines encryption with data theft and threats to publish stolen information, allowing pressure on victims to continue after systems are restored,” he explained.
Mackay Sugar’s disruption shows why a recovery plan needs to reflect the production calendar and dependencies on growers and contractors, Caron said.
“A technically sound restoration can still come too late for the business,” he said.
“Partners that understand those constraints can make better recommendations, prioritise the right systems and test whether recovery plans meet the client’s actual needs. That knowledge is a valuable part of the service.”
New CISO on the block
Caron began his role at Acronis this month, he told CRN Australia his focus for the upcoming year has three pronged-approach.
“First, strengthening Acronis’s own security posture as a company — we have a responsibility to lead by example. If we’re asking customers and partners to trust us with their data and their protection, our own house has to be beyond reproach,” he said.
“We must keep improving as the threat landscape changes.”
Caron said he wants to “deepen the impact” of the Acronis Threat Research Unit, the company's in-house cyber research team.
“Our research team can produce threat intelligence that informs our products and helps the broader community understand and respond to threats, particularly in the Asia Pacific region,” he explained.
“That means delivering timely, actionable findings to the people who can use them.”
For Caron, the most important task for him is helping Acronis’ partners navigate the complexity problem.
“Organisations can reduce operational complexity by simplifying their security stack rather than continually adding tools. My goal is to help Acronis partners consolidate tools and deliver broad protection with less management overhead,” he said.
“I have always said, ‘tools need to work for you, you shouldn't be working for the tools.' They must be effective and sustainable to manage. I look forward to helping Acronis put these priorities into practice,” he ended.