Partners urged to prepare customers for quantum “Q-Day” threat
The Q-Day goal posts could change — so the time to get started is now.
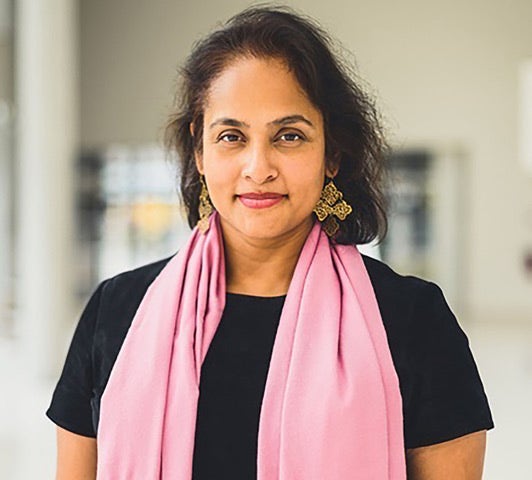
Organisations and their partners, need to start preparing, assessing critical processes and third-party dependencies, and requiring vendors and service providers to plan for post-quantum readiness, according to Dr Jaya Baloo, CISO and founder of Aisle.
Q-Day, the hypothetical day when a quantum computer can break widely used public key cryptography, is the focus. The Australian Signals Directorate (ASD) recommends organisations transition to post-quantum computing by the end of 2030.
“It’s making sure you have a plan for how the post-quantum algorithms can actually be put in there, and not break anything,” said Baloo, speaking from this year’s ISC2 Security Congress in Denver.
DigiCert’s second annual Quantum Readiness Outlook released in mid-2026 found around half of organisations surveyed (including in Australia) have undertaken quantum risk assessments, developed transition plans or created cryptographic inventories.
Baloo said a cryptographic inventory is a useful starting point, but organisations also need to map their specific risks.
“The main challenge is linking cryptographic use to business risk and testing replacements for compatibility and performance,” she said.
Baloo recommends that partners and managed service providers start to secure their own systems so they can help customers transition. It requires a staged plan, with three, six, 12-month milestones, but the key is getting started.
“You don’t want to be in a place where you won't succumb at the last minute to FUD [fear, uncertainty and doubt] … you're only susceptible when you haven't prepared,” Baloo explained.
Her advice is to start with systems closest to the perimeter, then identify shared components or systems and then apply more broadly to prioritise changes across the organisations.
“Reachability first, then look at where there’s some sort of concentration risk, and then try to apply it to a wider scale of your operations,” she said.
Baloo urges organisations in the same sector to band together by identifying common dependencies and applying coordinated pressure to suppliers and vendor to update tools for post-quantum readiness.
“The third parties that you’re dependent on are usually the same. If five of you have [a tool] that’s not going to be post-quantum ready, you can all apply pressure on that one manufacturer,” she said.
Above all, Baloo’s advice is for organisations and partners to avoid tying readiness to a predicted date for a general-purpose quantum computer — because the goalposts are moving. Advances in methods or mathematics could bring Q-Day closer — and the risks sooner.
“We’re assuming that only a general-purpose quantum computer can break RSA using Shor’s algorithm. But what if fundamental math problems lead to a different way to attack RSA? That means we don’t have till 2029 or 2030,” she ended.
Rosalyn Page travelled to Security Congress as a guest of ISC2.